Showing posts with label recovery. Show all posts

2014/04/16

Powershell wrapper for Beta Veeam Explorer for Active Directory

The new Veeam Explorer for Active Directory is cool stuff. I blogged about it earlier, showing how you can use it today. However it also shows that some manual steps have to be taken. Well, if you work as a sales engineer, you got to do these demo's a lot, meaning a lot of repetitive steps.

Then today, something on the Veeam forum inspired me. A guy was trying to start a Windows FLR via Powershell. So I decided to make a small wrapper to start the FLR and automate all those manual steps... well it sorta got "out of hands"..

You can get the wrapper script here. Save it on the backup server. Make sure to unblock the powershell script (go to the files properties, under the general tab, just above the ok button there should be some warning about downloaded content). Also make sure you have the correct executionpolicy setup.

Then create a new shortcut. In this shortcut specify the following parameter
powershell.exe -file "[path\to\script]\start-vbradrestorefromlatestbackup.ps1"

You can notice in the screenshot I added some parameters. This is where things got "out of hands".

-server [server] : auto select a certain vm. If you don't specify it, the wizard should propose you all the possible VM's in the backup files known to your backup & replication instance


-latest : auto select the latest restore point. If you don't specify it, the wizard should propose the available restore points for the VM you selected


 -autodiscovery : try to connect to the production server to learn where the ntds.dit file is stored. By default it is disabled and the wizard will use the default path "c:\windows\ntds\ntds.dit". I felt it was safer not to automatically connect to production. Notice that WinRM should be enabled as the script uses invoke-command to read the registry key on the production server.

-autodiscoveryserver [dns production ad] : give the ip or dns name to connect to, to do the auto discovery. If not specified but autodiscovery is on, the wizard will try to extract the DNS name from the restore point or use the VM name as a DNS name

-askcredentials : ask for credentials to do the autodiscovery. If you don't specify, it will just use invoke-command with your credentials.


-filepath : if you want to manually specify the path to the ntds.dit file (assuming you didn't enable autodiscovery)

-adexplorer : if you didn't installed the explorer on the default path

Once you have the shortcut, you should right click it and make sure to run it is as an administrator


If you want to give it a shiny icon, you can do that in the shortcut settings as well. Change the icon and browse to the explorer path. By default it is under "C:\Program Files\Veeam\Backup and Replication\ActiveDirectoryExplorer\Veeam.ActiveDirectory.Explorer.exe"


Now you should be up and running. Just click your shiny new shortcut. It should launch the wizard and automatically load the ntds.dit file after a FLR into the VEAD.


You will notice the Powershell window will stay open. That is because it is waiting for you to close the VEAD and to automatically stop the FLR so that everything is cleaned up as well


2014/03/17

Test driving the new Veeam Explorer for Active Directory

If you are a Veeam fan, you certainly need to read the word of Gostev. Basically you enroll  on the forum and every week you will get a mail from the forum containing the word of Gostev. He is the product manager for Backup & Replication and if you want to be the first one to know all about the new stuff in IT (not only Veeam), you'll see that this weekly mail avoids you reading 25 blog articles a day (quote I borrowed from one of my colleagues ;)).

This week wasn't any different. Veeam launched the public beta for the Veeam Explorer for Active Directory. So what is the big difference between the AD AIR wizard and this one? Well you don't need to power on a virtual lab to extract a single user. Instead, Veeam will read the ntds.dit (ad database file) directly via a file level recovery. This reduces recovery time drastically. The coolest part? It's a public beta, so everybody can test it!

So how do you get started? Well you will need a Veeam Backup & Replication server v7 installed. Then you can download the beta via the forums:
http://forums.veeam.com/veeam-backup-replication-f2/veeam-explorer-for-active-directory-t21038.html

Basically, you will get a zip file and in it is an MSI installer you can just next-next-install.


After that you should find the VEAD in your start menu


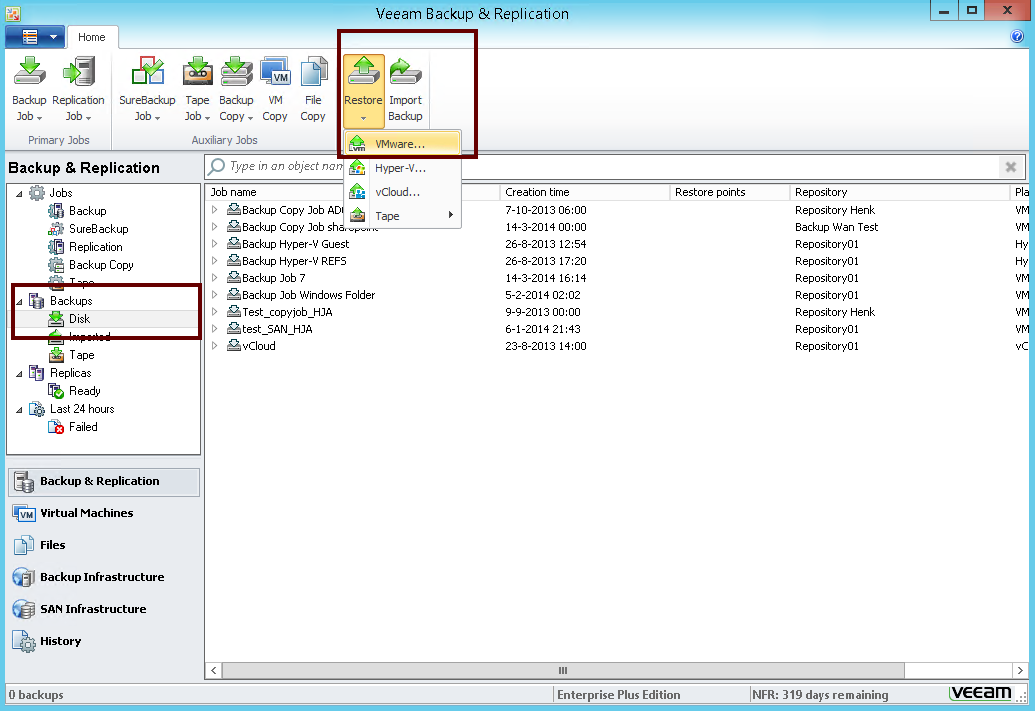
Now how do you get started? Well like with all explorer beta versions (exchange, sharepoint), you will need to start a file level recovery and point to the database. So lets start with the easy part, the file level recovery. Go to the main menu and choose restore.


Then choose to do a windows guest file level recovery


Find your active directory server


And start the guest files recovery wizard


Remember when you click finish, the recovery wizard will start but not any files will be actively recovered to your original machine.


Now you should see the file browser. But actually Veeam mounts the file level recovery under:
C:\VeeamFLR\\Volume

In my case the c: drive is
C:\VeeamFLR\ad02\Volume1

Keep the FLR wizard open during the whole process, otherwise Veeam will dismount the disk.

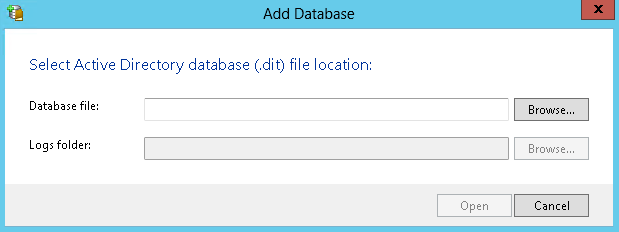
Now start the VEAD and click add database


Now you should point to the the ntds.dit file


I first tried to do a search through "C:\VeeamFLR\ad02\Volume1". This gave me 2 results:


But when I tried to mount the one in system32 I got the following error:


Luckily somebody already posted the solution on the forum. To find the correct path, go to your production server and look into:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\NTDS\Parameters

However since my ad02 server is a core server, I created this small script you can invoke remotely to find the path
$server = "ad02"
Invoke-Command -computer $server { Get-ItemProperty -path "Registry::HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\NTDS\Parameters\" }
This should show you the correct path under "DSA Database file"


So this says the file should be under C:\Windows\NTDS\ntds.dit. If we match this to the file level recovery path, we will get something like this:
C:\VeeamFLR\ad02\Volume1\Windows\NTDS\ntds.dit

Now again try to add the database file and point to the correct file:


After loading the db, the VEAD should show you your AD structure:


So lets try to restore a user. First of all you can easily see your attributes by right clicking the user:


Opening the attributes, I was wondering where they hid the recovery for individual attributes. Well it is actually part of the user recovery wizard. So lets follow the restore wizard:


First define the  AD to restore to and the credentials to use


Then specify where to restore the user


In the next step you can decide what to restore


This is the "twist" about the wizard, you can actually recover the user with the password. So if by accident you deleted a user during the night, you can recover him and next day, the end user won't even notice that he was deleted.


 Do you want to enable the account? :)


Final step is to click the restore button.

What is also cool is that not only can you restore an individual user, but also a whole OU if required:


Another great thing about it, is that it should be exchange aware. So if you restore a user, it should connect it to the correct mailbox as well.

So have fun playing with the beta! And remember kids, it's a beta, don't test it in production :)